








 CryptoSlate
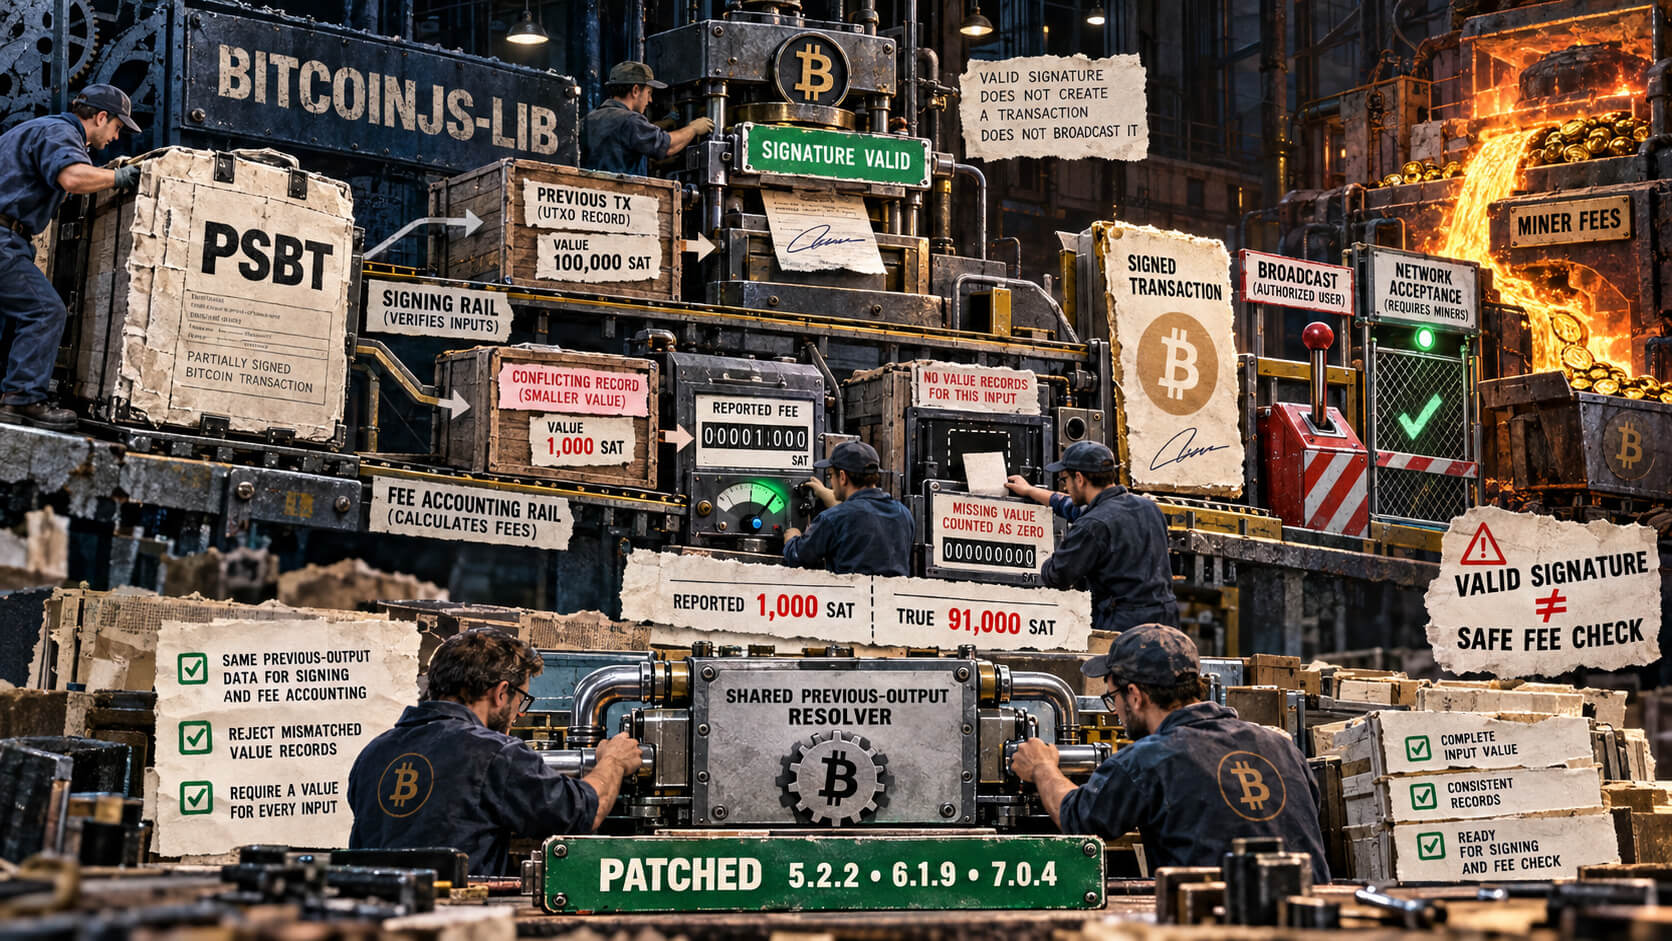


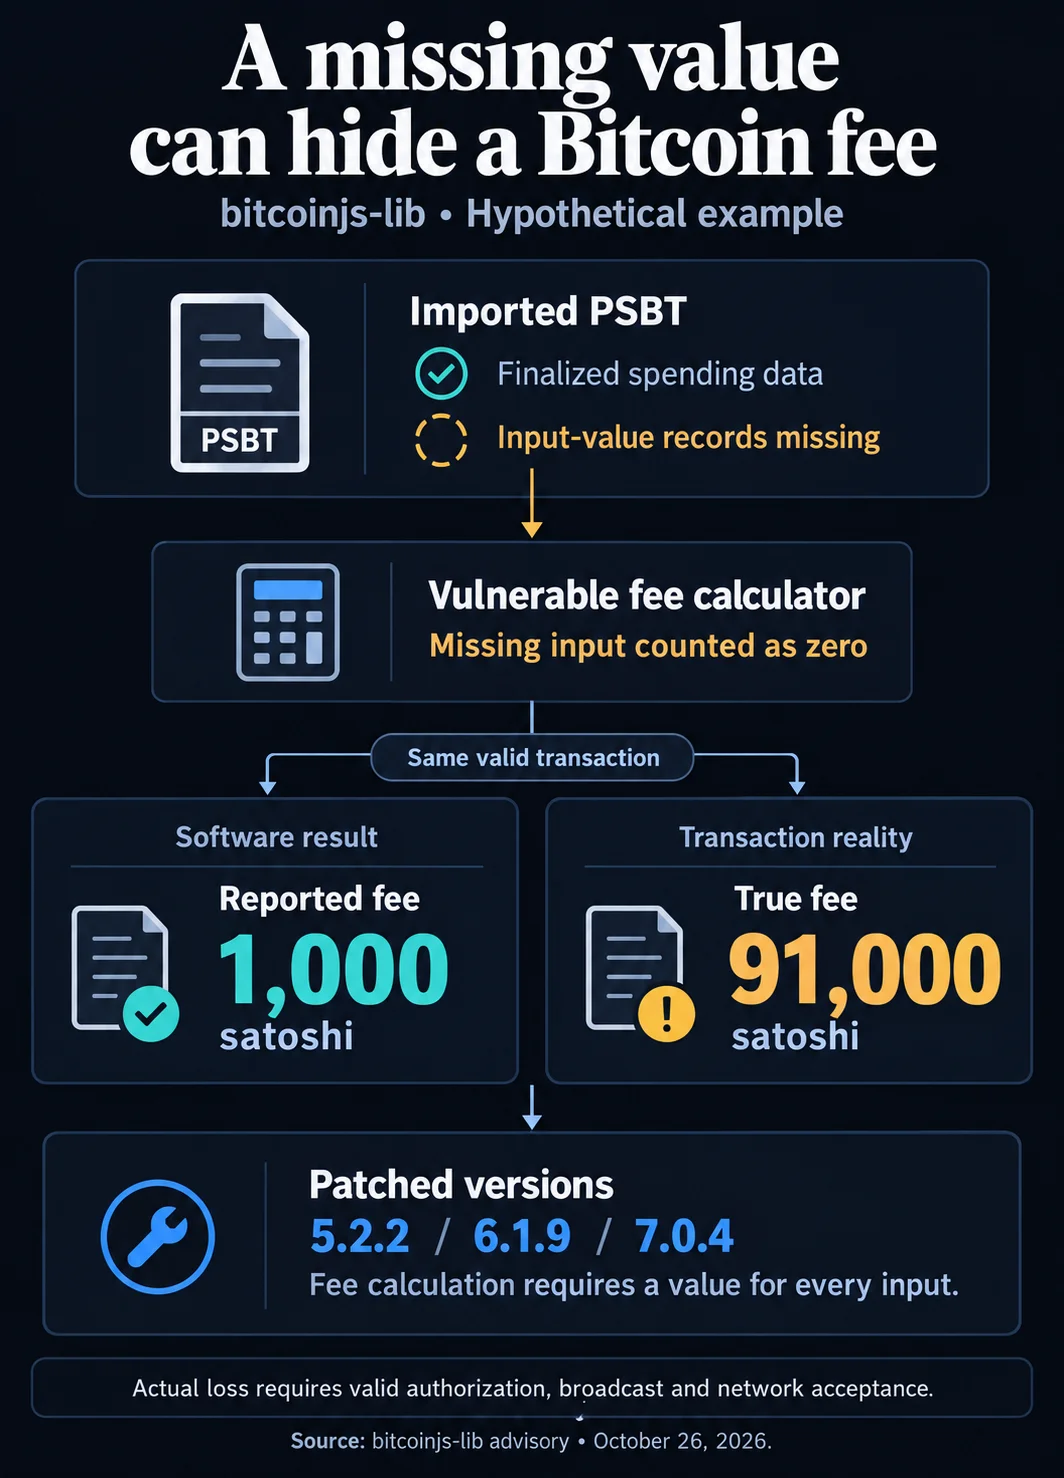
Two bitcoinjs-lib vulnerabilities can make applications understate the miner fee on a valid Bitcoin transaction. The Oct. 26 advisories list fixes in versions 5.2.2, 6.1.9 and 7.0.4. The affected workflow uses partially signed Bitcoin transactions, or PSBTs, where applications pass transaction data and signatures between clients.
In one flaw, signing and fee accounting can use different values for the same input. A demonstration on bitcoinjs-lib 7.0.1 showed an actual fee of 900,000,000 satoshi reported as only 200 satoshi, allowing the transaction to pass the default fee-rate warning. The second flaw involves finalized inputs with missing value records. Its hypothetical example showed a true fee of 91,000 satoshi reported as 1,000 satoshi.
Why it matters
The bugs do not create signatures or authorize transfers by themselves. Loss requires an authorized, valid transaction to be broadcast and accepted by the Bitcoin network, with the excess value paid as a miner fee. The risk is concentrated in applications that trust bitcoinjs-lib's fee calculation or excessive-fee safeguards without independently verifying the outputs being spent.
Affected releases include 5.2.0 through 5.2.1, 6.0.0 through 6.1.8 and 7.0.0-rc.0 through 7.0.3 for the conflicting-record flaw. The missing-record flaw also reaches 5.1.0 through 5.2.1.
Market impact
This is an application and wallet security issue rather than a Bitcoin consensus failure. Maintainers should upgrade to the patched releases, reject conflicting input values or scripts, and verify every input value before signing, trusting fees or extracting a transaction.
The remediation gives signing and accounting a shared method for resolving previous outputs, requires an amount for every input during fee calculation, and clears cached fees and extracted transactions after relevant metadata changes. Teams unable to upgrade should independently verify referenced output values.

Frequently asked questions
-
What did bitcoinjs-lib patch?
It patched two bugs that could make applications understate miner fees when processing partially signed Bitcoin transactions.
-
How large was the fee discrepancy in one demonstration?
A demonstration on bitcoinjs-lib 7.0.1 showed an actual fee of 900,000,000 satoshi reported as 200 satoshi.
-
Can the vulnerabilities move Bitcoin without a signature?
No. The defects do not create signatures or authorize transfers. Loss requires an authorized, valid transaction to be broadcast and accepted.
-
Which bitcoinjs-lib versions contain the fixes?
The advisories list fixes in versions 5.2.2, 6.1.9 and 7.0.4 for their corresponding release lines.
-
What should maintainers do if they cannot upgrade?
They should independently verify referenced output values, reject conflicting records before signing or trusting fees, and verify every input value before extracting a transaction.
 WatcherGuru
 Crypto Capital Venture
 CoinDesk
 CoinTelegraph
 TheBlock
 Crypto News
 Glassnode