








 CryptoSlate

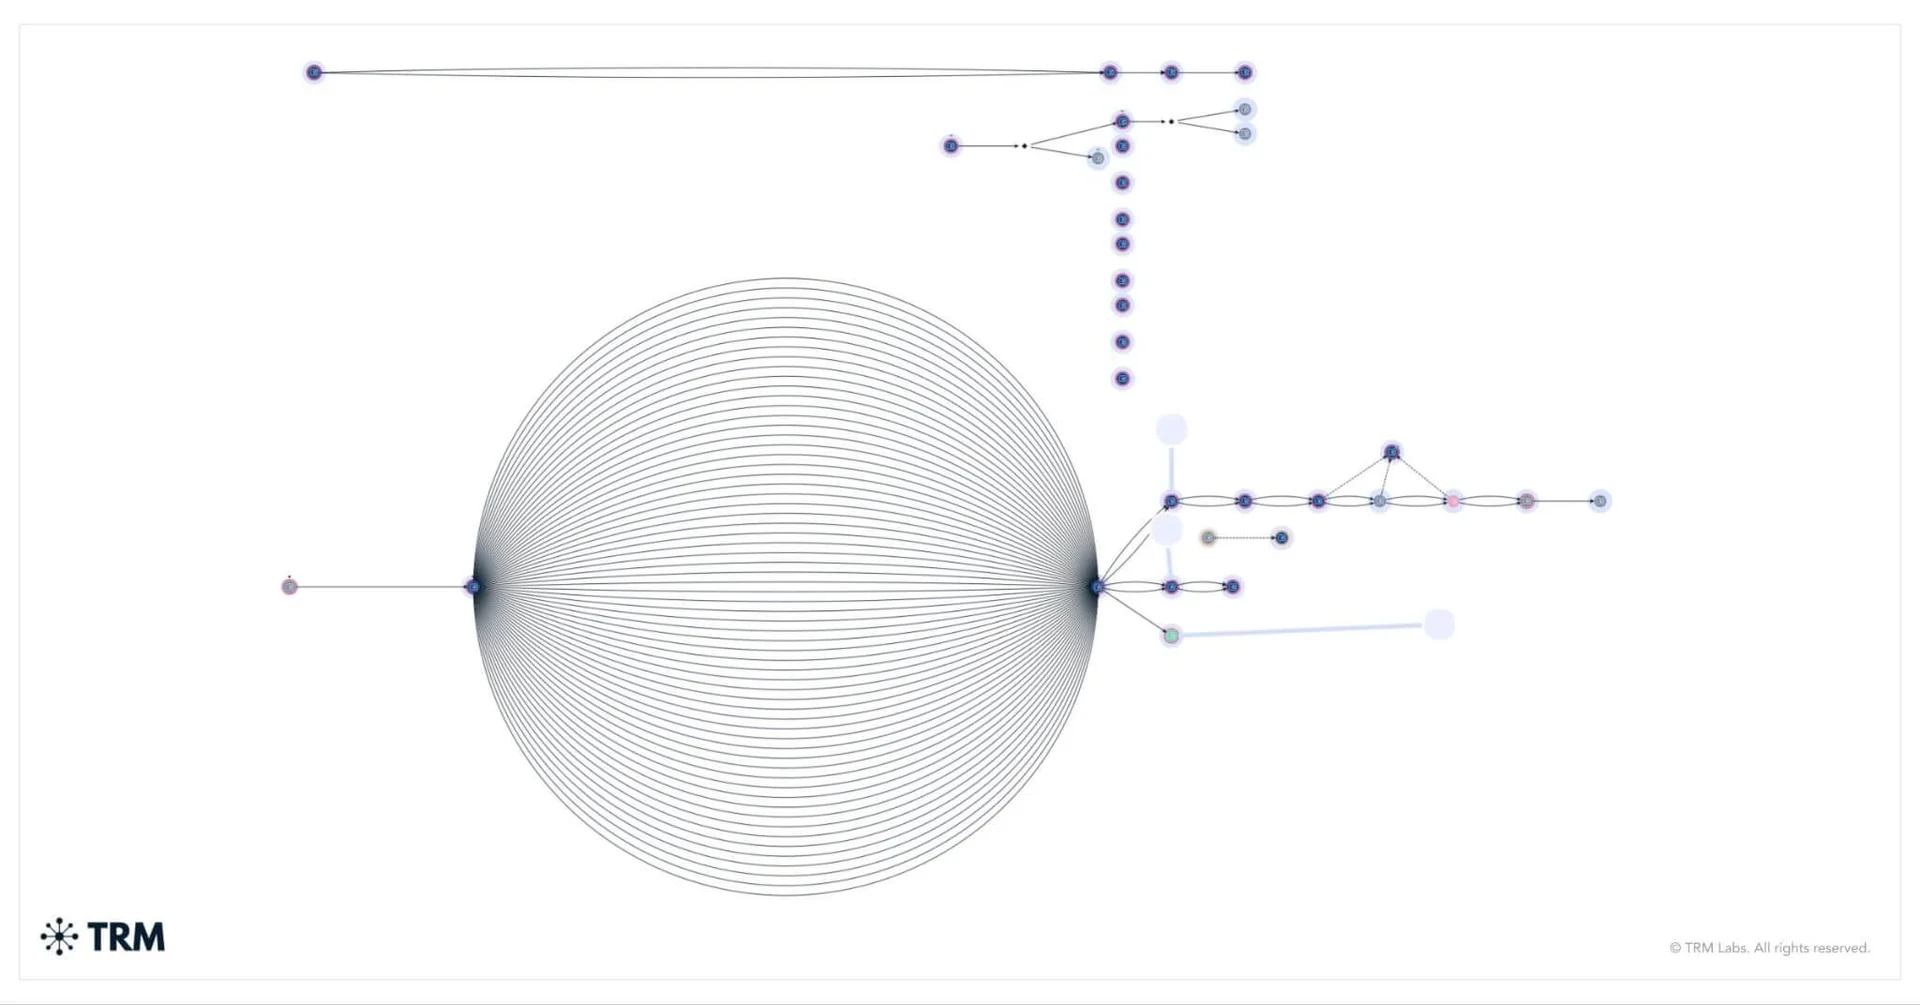

Binance-linked wallets on the XRP Ledger transferred about 233.46 million XRP, worth $296 million, between 20:05 and 20:09 UTC, opening an attack that TRM Labs traced across 10 blockchains. The attacker had spent at least 36 hours preparing, and investigators tracked approximately $6.36 billion in transfers by 00:30 UTC on Oct. 30.
Why it matters
TRM traced preparations to Oct. 28, when an attacker-controlled wallet received three small transfers from Tornado Cash. The following day, the attacker deployed and tested malicious smart-contract code against newly created Ethereum wallets before rehearsing a successful transfer. The main operation began about four hours after the final rehearsal.
Most funds left Binance-linked wallets within roughly 20 minutes. The attack spread across Ethereum, Bitcoin, Tron, the XRP Ledger, Solana, Arbitrum, Optimism, Base, Avalanche and Polygon. On Ethereum, 50 previously signed EIP-7702 authorizations let a Binance hot wallet delegate execution to a malicious contract, which swept 167,464 ETH and 63 tokens. Other transfers included 18,270 BTC and, on Tron, 612.7 million USDT and 46.4 million TRX.
Market impact
The investigation describes a coordinated, multi-chain operation, with further wallet sweeps continuing for hours. TRM’s reconstruction does not resolve how the attacker obtained the authorizations: researcher Derek Chiang said the possibilities include stealing the wallet’s private key or tricking its owner into signing a malicious authorization. The incident puts authorization controls and hot-wallet security in focus for exchanges and users alike.


Frequently asked questions
-
How much did the first XRP transfers amount to?
Binance-linked wallets transferred approximately 233.46 million XRP, valued at $296 million, between 20:05 and 20:09 UTC.
-
How long did the attacker prepare before the operation?
TRM Labs traced at least 36 hours of preparation, including testing malicious smart-contract code on newly created Ethereum wallets.
-
How did the Ethereum wallet sweeps work?
The attacker submitted 50 previously signed EIP-7702 authorizations, allowing a Binance hot wallet to delegate execution to a malicious contract that swept 167,464 ETH and 63 tokens.
-
Which blockchains did the transfers span?
TRM traced transfers across Ethereum, Bitcoin, Tron, the XRP Ledger, Solana, Arbitrum, Optimism, Base, Avalanche and Polygon.
-
How did the attacker obtain the required authorizations?
The method remains unresolved. Researcher Derek Chiang said possibilities include obtaining the wallet’s private key or tricking its owner into signing a malicious authorization.
 TheBlock
 WatcherGuru
 CoinDesk
 Lookonchain
 CoinTelegraph