


 WuBlockchain
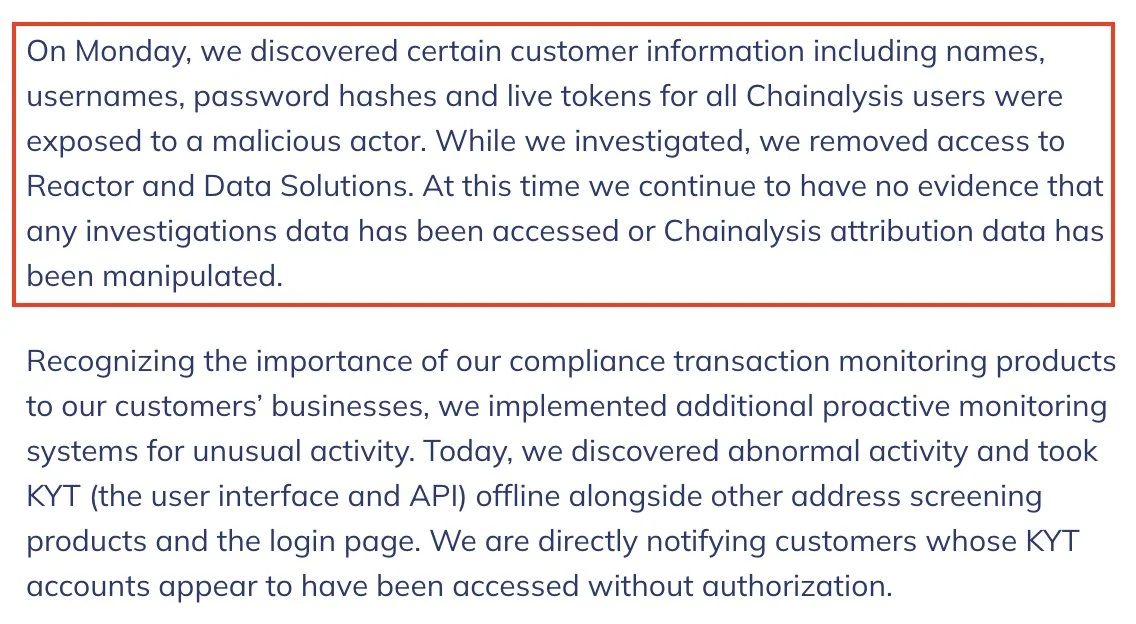
Chainalysis said an attacker obtained names, usernames, password hashes and valid authentication tokens belonging to all users. Some customers' plaintext passwords were also exposed through a separate attack method.
The blockchain analytics firm suspended its KYT transaction monitoring, address screening and login services after detecting abnormal activity. It required all users to reset their passwords and rotate API keys where necessary.
Why it matters
The updated disclosure expands the scope of the breach beyond the customer identity information Chainalysis initially confirmed. On October 30, the firm said it had found no evidence that passwords or session tokens had leaked. It attributed the breach to a hacker using offensive AI agent technology.
Market impact
The incident disrupted services used for transaction monitoring and address screening. The exposure of valid authentication tokens and some plaintext passwords also prompted account security measures across the user base.
Source: [Updated Nov 4: Chainalysis Security Incident Information](https://www.chainalysis.com/blog/security-incident-october-30/)
Frequently asked questions
-
What user information did the Chainalysis attacker obtain?
Chainalysis said names, usernames, password hashes and valid authentication tokens belonging to all users were exposed. Some customers' plaintext passwords were also leaked through a separate attack method.
-
Which Chainalysis services were suspended?
The company suspended KYT transaction monitoring, address screening and login services after detecting abnormal activity.
-
What security steps did Chainalysis require from users?
Chainalysis required all users to reset their passwords and rotate API keys where necessary.
-
How did the updated disclosure differ from the October 30 notice?
The initial notice confirmed access to certain customer identity information and said there was no evidence of password or session token leaks. The update disclosed exposure of password hashes, valid authentication tokens and some plaintext passwords.
-
What did Chainalysis say about the method used in the breach?
In its October 30 disclosure, Chainalysis attributed the breach to a hacker using offensive AI agent technology. It said some plaintext passwords were exposed through a separate attack method.
 CoinTelegraph
 Altcoin Daily
 CoinDesk
 Lookonchain
 TheBlock
 CryptoSlate