








 CryptoSlate


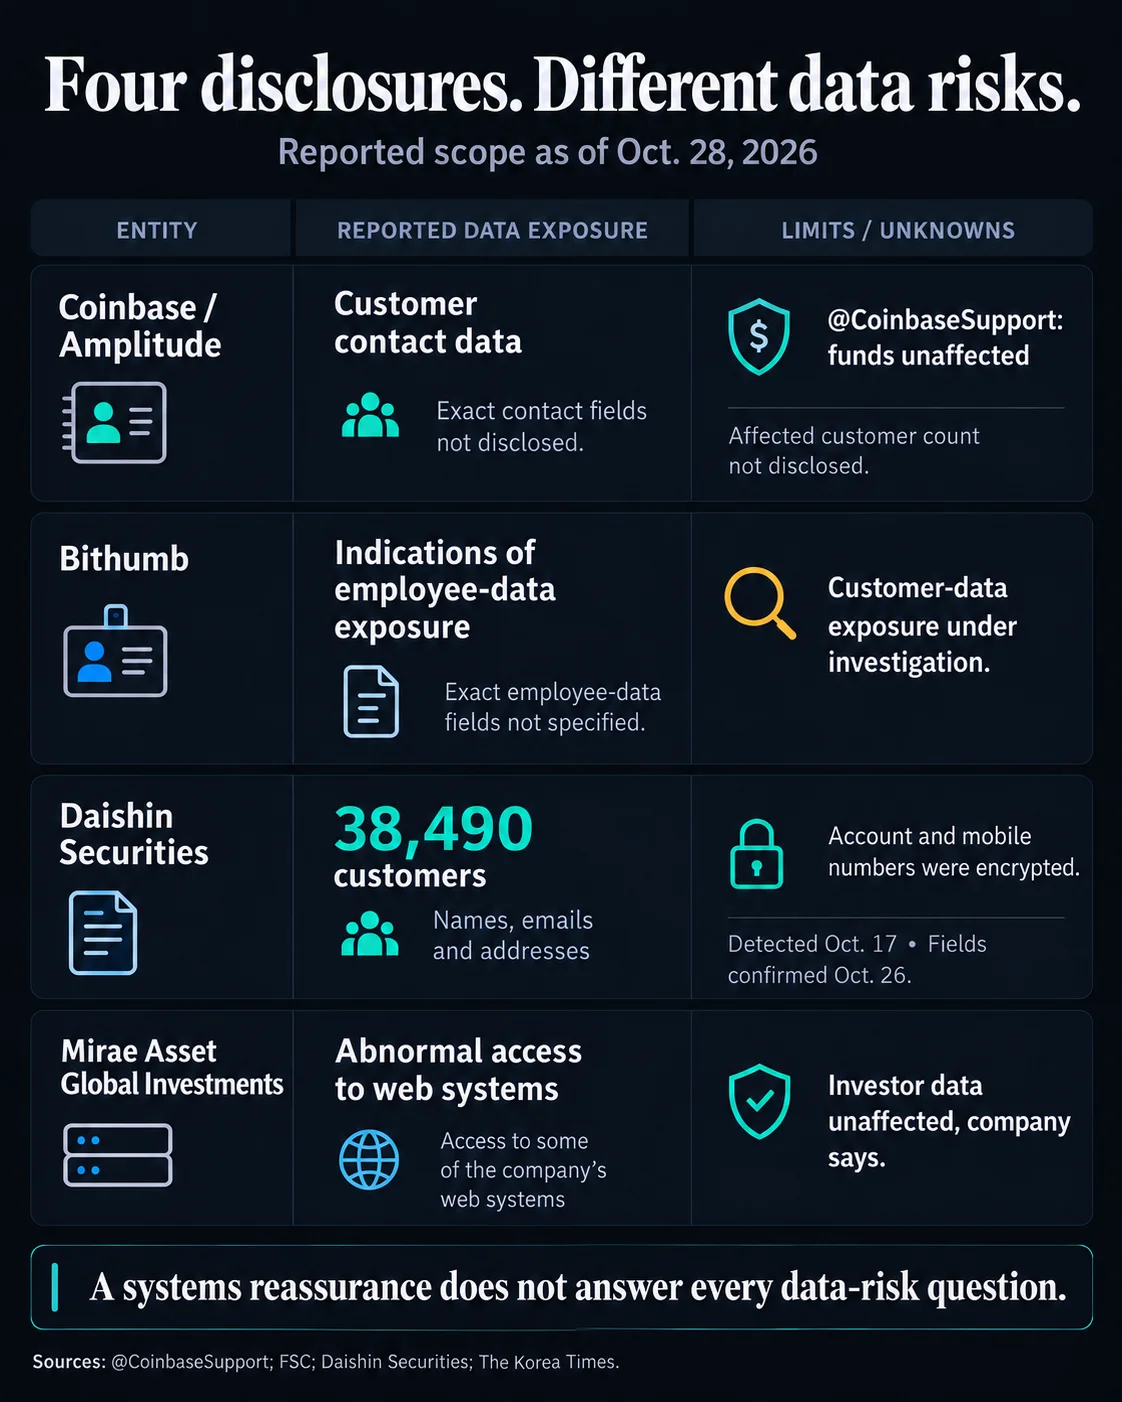
Coinbase said an incident at analytics provider Amplitude exposed contact information belonging to a small subset of its customers, but found no evidence that its own systems were accessed or customer funds put at risk. The exchange said Wednesday it was notifying affected customers and regulators, but did not disclose how many people were affected or which contact details were exposed.
Why it matters
The incident came alongside separate security disclosures involving South Korea's Bithumb, Daishin Securities and Mirae Asset Global Investments. Daishin said personal and financial information belonging to 38,490 customers was exposed. South Korean regulators opened investigations and held an emergency meeting after the incidents.
Leaked contact details can support phishing, SIM swapping and social engineering even when attackers do not reach core trading or custody systems. Binance founder Changpeng Zhao warned that criminals can combine leaked addresses with information about cryptocurrency holdings to target investors online or in person.
Market impact
The disclosures raise the security stakes for customers and financial firms beyond protecting funds held on an exchange. Bithumb is investigating whether customer records were accessed, while South Korea's Financial Services Commission said it had not confirmed exposure of wallet addresses or information that could enable fraudulent transfers.
Zhao recommended separate email aliases and phone numbers for exchange accounts, passkeys or hardware security keys instead of SMS authentication, and withdrawal restrictions. He also urged customers to review account sessions and API permissions and distrust unsolicited messages claiming to come from exchange support.
Frequently asked questions
-
What customer information did the Coinbase incident expose?
Coinbase said contact information for a small subset of customers was exposed through analytics provider Amplitude. The exchange did not specify which details or how many customers were affected.
-
Did Coinbase report unauthorized access to its systems or lost customer funds?
No. Coinbase said it found no evidence of unauthorized access to its systems and said customer funds remained secure.
-
How many Daishin Securities customers were affected?
Daishin Securities said personal and financial information belonging to 38,490 customers had been exposed.
-
Why can leaked contact information create risks even if funds remain secure?
Contact information can help criminals target people with phishing, SIM swapping and social engineering. Leaked addresses combined with information about crypto holdings can also raise physical security risks.
-
What account protections did Changpeng Zhao recommend?
Zhao recommended separate email aliases and phone numbers, passkeys or hardware security keys instead of SMS authentication, withdrawal restrictions, and regular reviews of account sessions and API permissions.
 Crypto News
 CoinTelegraph
 WuBlockchain
 CoinDesk
 TheBlock