


 CryptoSlate
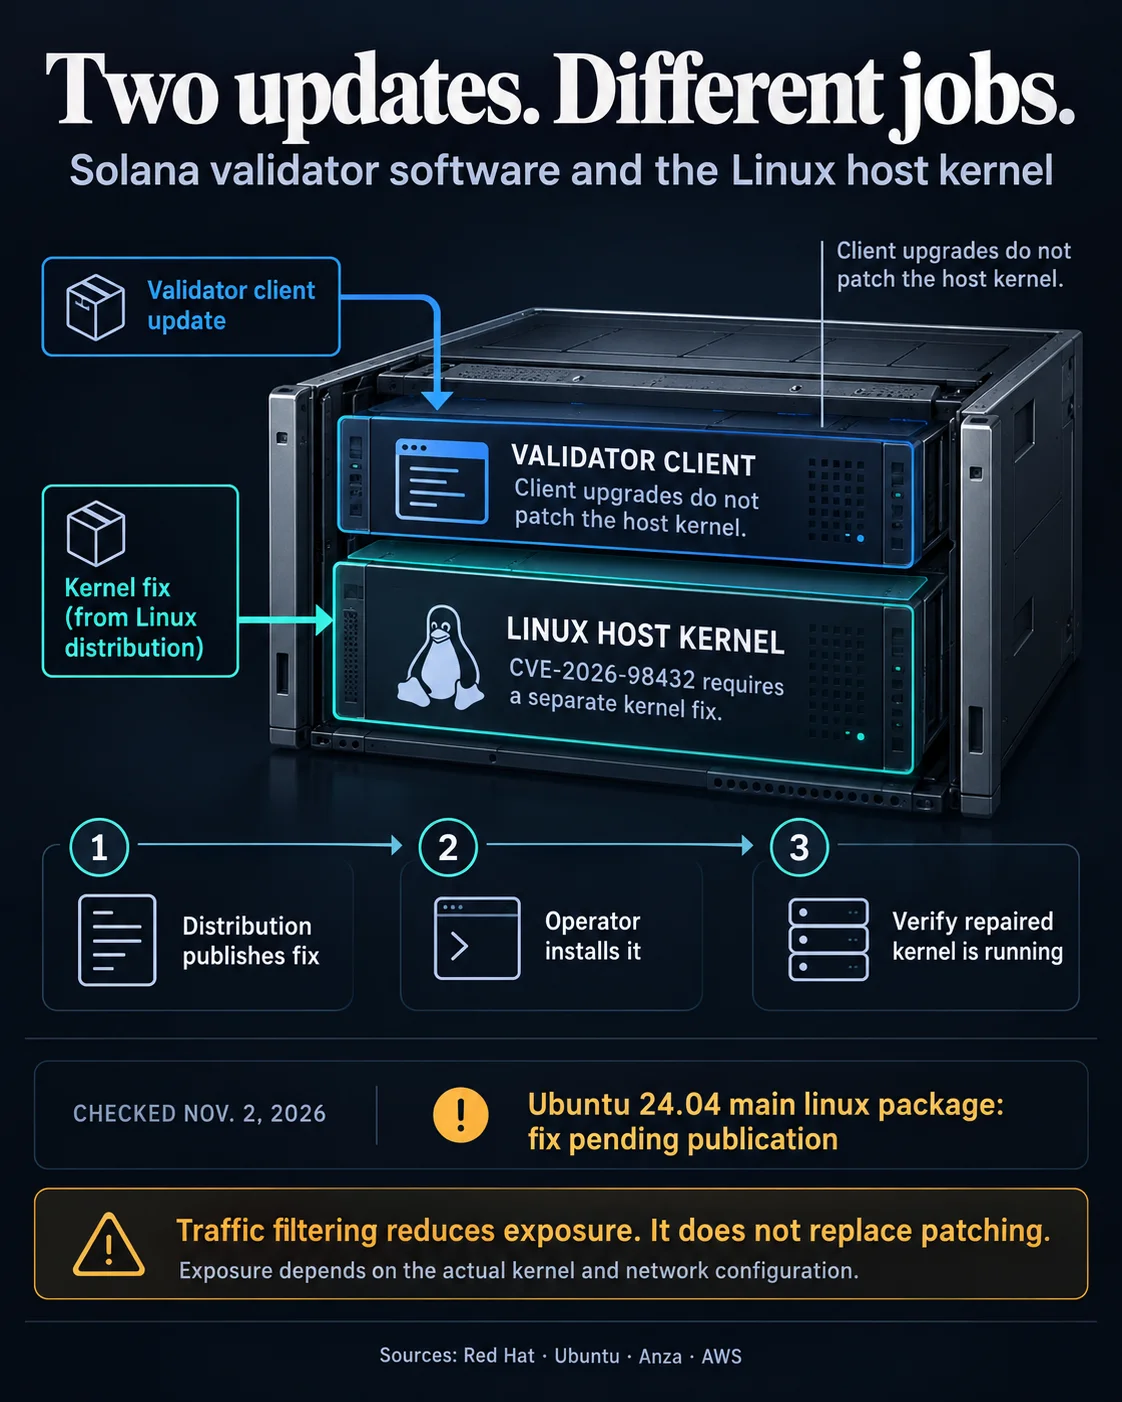

Anza urged Solana mainnet-beta validators to take immediate precautions against CVE-2026-98432, a Linux vulnerability rated 9.8 out of 10. Researchers demonstrated an attack that can grant root access to affected servers without credentials or user interaction. Ubuntu's security patch was still pending as of Nov. 2.
Why it matters
The flaw involves memory handling during IPv4 TCP connection processing. Anthropic disclosed on Oct. 27 that an unreleased Claude research model developed an exploit for Linux servers running an MPTCP listener. The demonstration took about 53 minutes to achieve remote command execution.
The demonstrated attack relies on a specific MPTCP configuration. There is no evidence that Solana validators have been compromised through the flaw, and the research does not show that every validator is vulnerable. Actual exposure depends on each server's kernel version and network configuration.
Market impact
Anza advised affected operators to block incoming TCP packets containing IPv4 options, disable Multipath TCP, and turn off TCP request-socket migration until a security update is available. Red Hat cautioned that blocking malicious IPv4 traffic cannot fully eliminate exposure and may disrupt some workloads.
Ubuntu's tracker listed its main Linux kernel package for Ubuntu 24.04 as “Vulnerable work in progress,” with version 6.8.0-149.149 identified as the planned fix. AWS said corrected packages were available for Amazon Linux 2 and Amazon Linux 2023, and told operators to update and reboot. Solana's validator requirements specify Ubuntu 24.04 and public IPv4 connectivity, but the number of validators running affected configurations remains unclear.
Frequently asked questions
-
How severe is the Linux vulnerability affecting some Solana validator setups?
CVE-2026-98432 is rated 9.8 out of 10. Researchers demonstrated remote root access without credentials or user interaction.
-
What configuration did the demonstrated exploit target?
The demonstrated attack targeted Linux servers running an MPTCP listener. The research does not establish that every Solana validator is vulnerable.
-
Have Solana validators been confirmed compromised by the flaw?
No. There is no evidence that Solana validators have been compromised through CVE-2026-98432.
-
What temporary protections did Anza recommend?
Anza advised affected operators to block incoming TCP packets containing IPv4 options, disable Multipath TCP, and turn off TCP request-socket migration.
-
Why does the Ubuntu patch status matter to Solana validators?
Ubuntu's security patch was still pending as of Nov. 2. Solana's validator requirements specify Ubuntu 24.04, though exposure depends on each server's kernel version and network configuration.
 CoinDesk
 WuBlockchain
 TheBlock