


 CryptoSlate
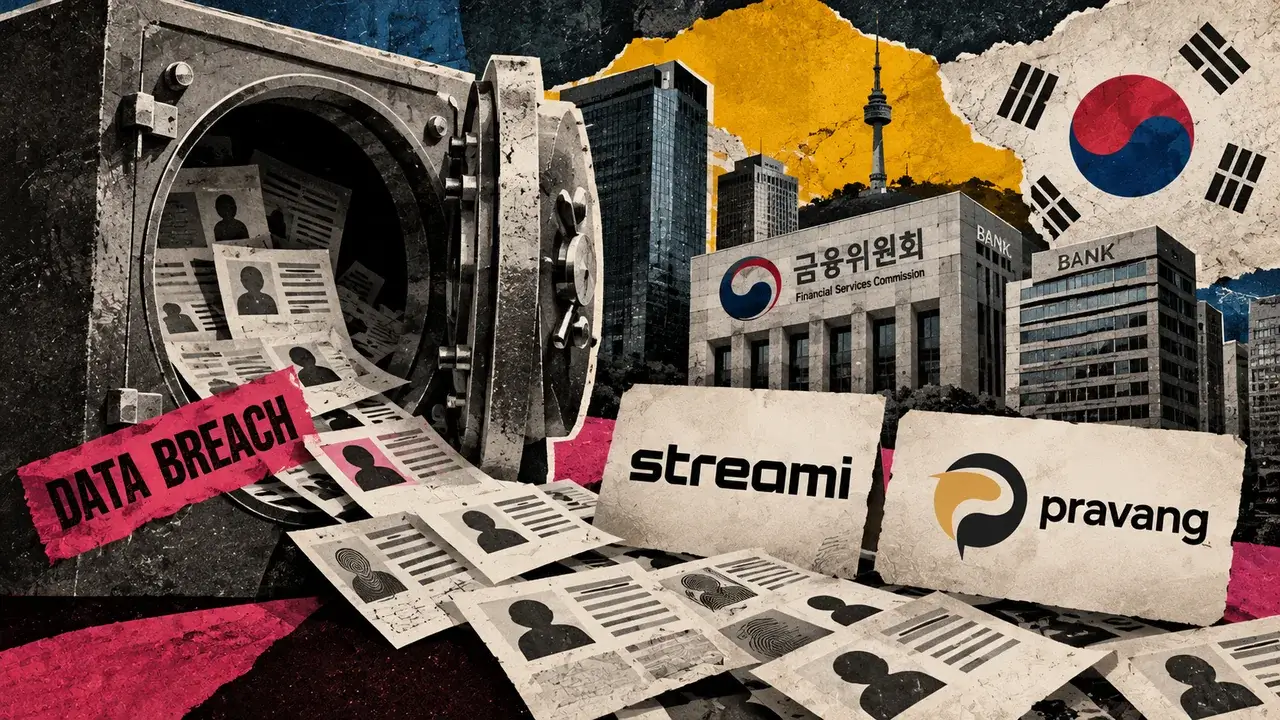
South Korea’s Financial Services Commission named crypto businesses Streami and Pravang among 16 financial companies hit by recent customer-data breaches. Streami operates the Gopax exchange. The FSC estimated about 100,000 data items were exposed across the affected firms, including names, contact details, resident registration numbers and email addresses, without a company-level breakdown.
As of the FSC’s October 14 disclosure, authorities had not identified leaked account passwords or credit card numbers. Investigators are examining the attack methods, whether the incidents were linked or involved a common attacker, and whether AI was used. The list of affected firms could grow as companies check their systems against attacker IP addresses shared by authorities.
Why it matters
A sector-wide self-assessment found security gaps beyond the confirmed breach list. Of 555 companies that completed a 12-point checklist, 130 reported areas needing improvement, mainly involving security patches and monitoring. Reported weaknesses included outdated software, unsupported systems, a lack of round-the-clock monitoring, and gaps in authentication or access controls. Companies submitted remedial plans and began corrective steps.
The findings put operational security and customer-data protection in focus for South Korea’s financial sector, including crypto businesses named alongside major banks. However, the FSC did not provide a company-level exposure count or specify whether each proposed measure will cover virtual asset businesses.
Market impact
The FSC plans wider inspections, faster threat-information sharing and more frequent vulnerability testing, with checks starting at larger financial companies. One proposal would require assessments at least twice a year, compared with the existing annual requirement for financial companies and electronic financial businesses. Regulators also proposed clearer executive accountability, more support for smaller firms and stronger sanctions. The detailed inspection scope and schedule remain unsettled.
Frequently asked questions
-
Which South Korean crypto businesses did the FSC name?
The Financial Services Commission named Streami, which operates the Gopax exchange, and Pravang among 16 affected financial companies.
-
What types of customer data were exposed?
The FSC estimated about 100,000 data items were exposed across affected firms, including names, contact details, resident registration numbers and email addresses.
-
Were account passwords or credit card numbers reported as leaked?
As of the FSC’s October 14 disclosure, authorities had not identified leaked account passwords or credit card numbers.
-
What did the wider security checklist find?
Of 555 companies completing a 12-point checklist, 130 reported areas needing improvement, mainly involving security patches and monitoring systems.
-
What security measures is South Korea considering?
The FSC plans wider inspections and faster threat sharing. One proposal would require vulnerability assessments at least twice a year, starting with larger financial companies.
 WatcherGuru
 TheBlock
 Crypto News
 CoinDesk
 CoinTelegraph
 WuBlockchain