


 WuBlockchain
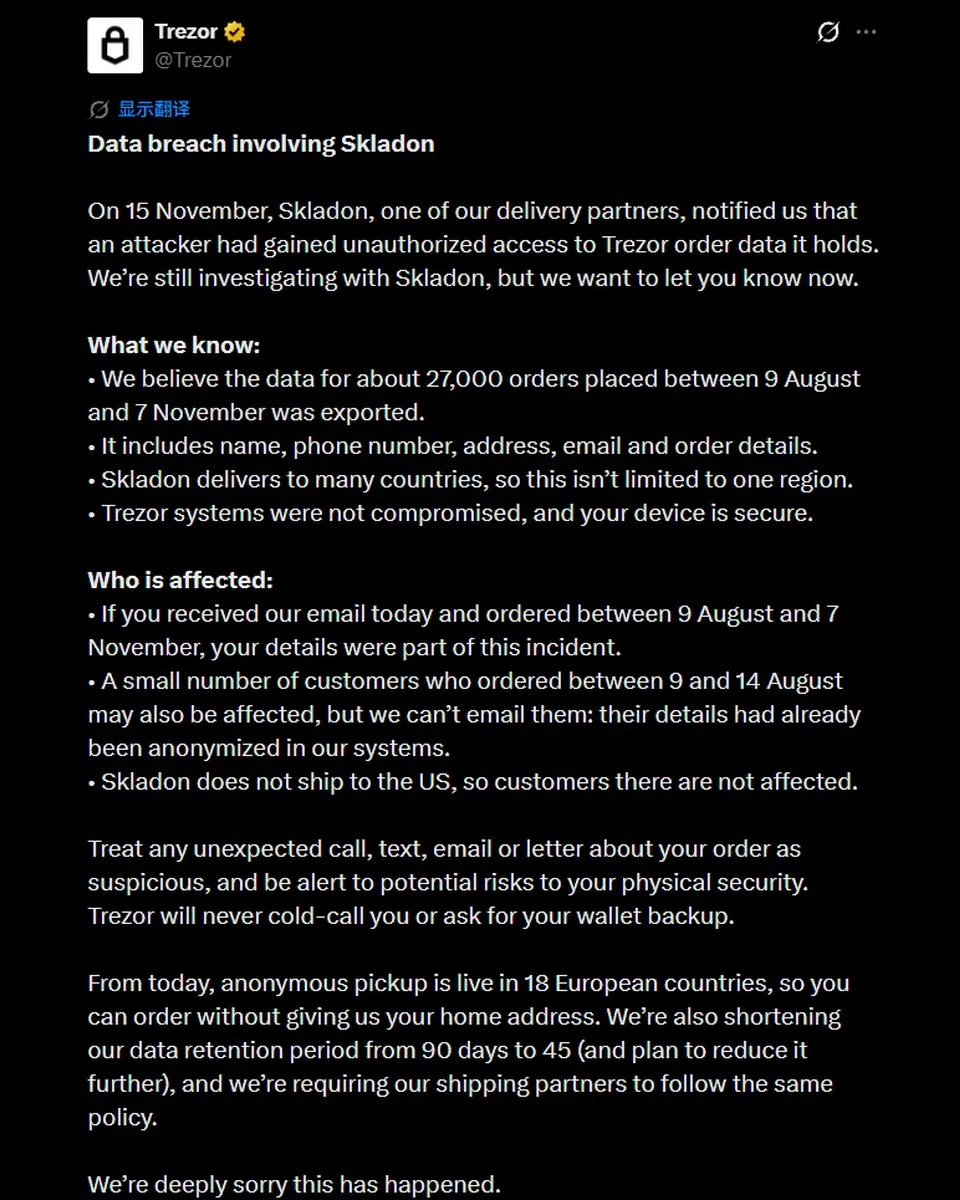
Trezor disclosed that a breach at shipping partner Skladon exposed personal information linked to approximately 27,000 orders placed between August 9 and November 7. The exported data was believed to include names, phone numbers, addresses, emails and order details, while Trezor said its own systems and hardware wallets remained secure.
Why it matters
The incident extends the cybersecurity risk facing hardware-wallet customers beyond the device itself and into the broader vendor ecosystem. Skladon said attackers accessed its systems and were believed to have exported customer information. The breach affected multiple countries, but not US customers.
Exposed contact and delivery details can give attackers material for targeted phishing, impersonation or attempts to pressure customers into revealing wallet information. Trezor warned affected customers to watch for fraudulent messages and potential physical-security risks.
Market impact
The key distinction is that the breach concerns shipping records, not a compromise of Trezor wallets or the company's internal systems. There is no reported loss of seed phrases, private keys or wallet assets. The practical impact is privacy and operational security for affected customers, particularly those who have not checked whether exposed names, addresses or order details are being used in scams.
Frequently asked questions
-
What information was exposed in the Trezor shipping-partner breach?
The exported data was believed to include names, phone numbers, addresses, emails and order details linked to approximately 27,000 orders.
-
Were Trezor's hardware wallets or customer assets compromised?
Trezor said its own systems and hardware wallets remained secure. The report did not identify any compromise of seed phrases, private keys or wallet assets.
-
Were US customers affected by the Skladon breach?
The breach affected customers in multiple countries, but Trezor said US customers were not affected.
-
When were the affected Trezor orders placed?
The affected orders were placed between August 9 and November 7. Skladon notified Trezor of the intrusion on November 15.
-
What risks do Trezor customers face from the exposed data?
Trezor warned of phishing scams and potential physical-security risks. Customers should verify unusual requests through trusted channels and avoid suspicious links.
 CryptoSlate
 CoinDesk
 TheBlock
 CoinTelegraph
 Crypto Rank News
 Crypto News
 Lookonchain