


 CryptoSlate
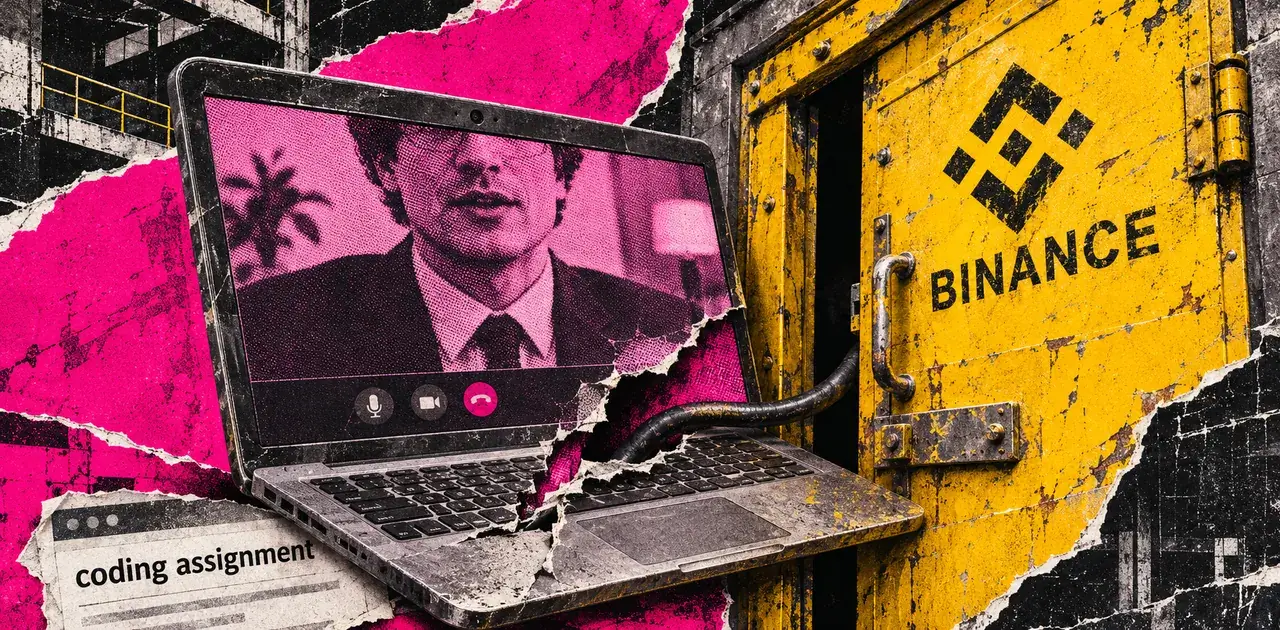

Binance said it thwarted 57 suspected North Korea-linked cyber threats in 2026, but attackers breached its systems through a fake job interview and accessed wallet infrastructure involved in a $6.34 billion crypto theft on Oct. 29. The exchange described the attack in a Nov. 3 security report, and the FBI attributed the theft to North Korea's TraderTraitor operation.
Why it matters
The breach began with a recruitment scam targeting engineers. Attackers posed as employees of a fictitious company, conducted staged video interviews, then persuaded an engineer to download a coding assignment containing malware. The malicious software evaded endpoint defenses, and attackers later used a compromised computer and an internal AI tool to gain control over two more engineers.
They obtained a container deployment permission token and used stolen credentials to deploy a malicious container, reaching Binance's wallet-signing infrastructure. Binance said the attackers initiated transfers outside its normal withdrawal process across several blockchain networks.
The tactics were not entirely new. The FBI had warned in 2024 about North Korean hackers using personalized job approaches to infiltrate crypto businesses. Researchers also documented similar fake-interview and malicious coding-assignment campaigns in 2026. Binance said it had detected and prevented dozens of suspected threats, including campaigns involving fraudulent interviews and compromised developer tools, but did not disclose how many of those cases matched the successful operation.
Market impact
The incident highlights a security gap between recognizing a threat and preventing a compromised employee account from reaching critical wallet systems. Binance said it replaced compromised devices, revoked exposed credentials, rebuilt affected wallet infrastructure, strengthened developer-environment protections and expanded AI-based behavioral monitoring.
For crypto platforms, the attack underscores that recruitment processes and developer tools can become paths into custody infrastructure.
Frequently asked questions
-
How did the attackers use a fake job interview to breach Binance?
They posed as staff at a fictitious company and sent an engineer a coding assignment containing malware. The malicious software evaded endpoint defenses and enabled access to Binance systems.
-
How did the attackers reach Binance's wallet infrastructure?
They used a compromised computer and an internal AI tool to gain control over two more engineers, then obtained a container deployment permission token and deployed a malicious container.
-
What did the FBI say about the crypto theft?
The FBI attributed the Oct. 29 theft to North Korea's TraderTraitor operation, which it described as part of an effort to steal cryptocurrency and launder proceeds through decentralized finance platforms.
-
What security steps did Binance say it took after the breach?
Binance said it replaced compromised devices, revoked exposed credentials, rebuilt affected wallet infrastructure, strengthened developer-environment protections and expanded AI-based behavioral monitoring.
-
Why does the incident raise questions about Binance's security defenses?
Binance said it had prevented 57 suspected North Korea-linked threats, yet attackers still used a fake recruitment process to reach wallet-signing infrastructure. The exchange has not disclosed how many prevented cases involved similar tactics.
 CoinDesk
 TheBlock
 WuBlockchain
 Crypto Rank News