


 CryptoSlate
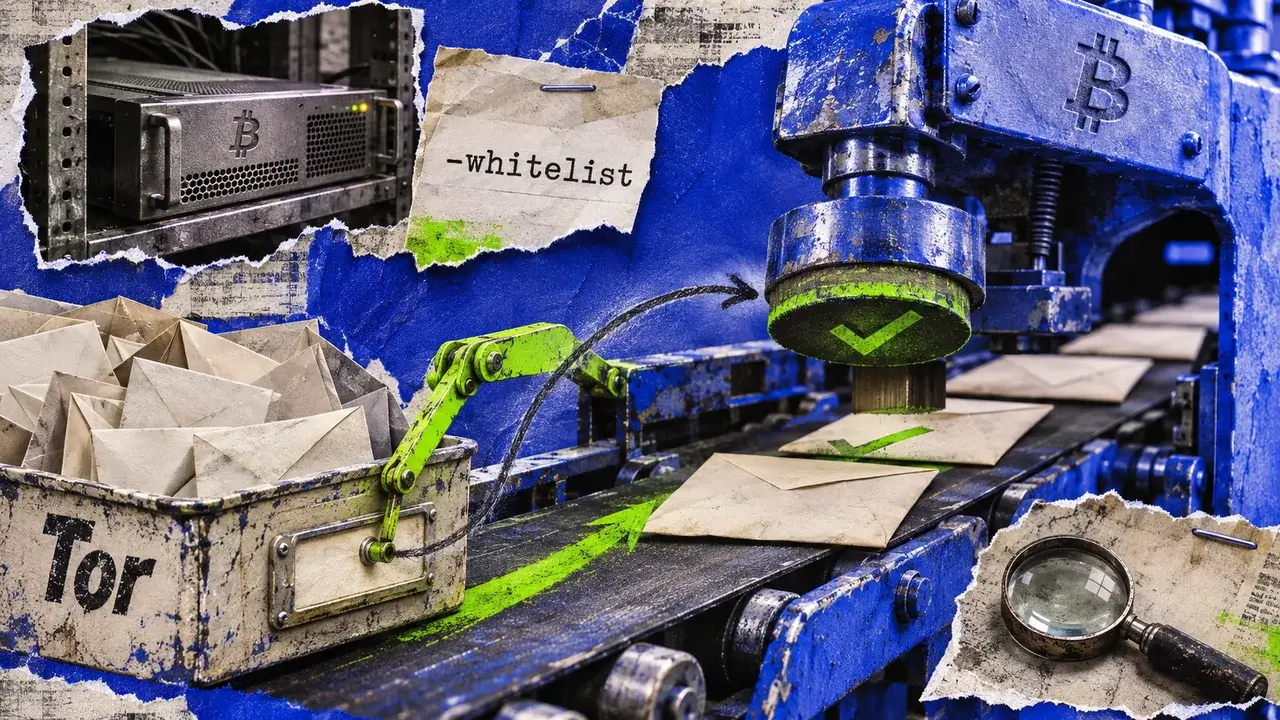
Thousands of reachable Bitcoin mainnet nodes treated incoming Tor connections as trusted peers because of a Bitcoin Core configuration flaw, the project disclosed on Nov. 10. Rated medium severity, CVE-2025-62860 affected vulnerable software only when a non-default whitelist included the IP address of the node's Tor daemon. Nodes without that setting were unaffected.
Why it matters
Bitcoin Core sees the Tor daemon's IP address rather than the remote peer's actual address. On affected configurations, a whitelist matching the daemon caused incoming Tor connections to inherit permissions intended for trusted peers. Those permissions exempted connections from some denial-of-service limits and privacy protections.
Popular vendors bundled node software with Tor and a matching whitelist range, while some client software also required whitelisting and commonly ran alongside Tor. The privileges described in the disclosure do not establish wallet access or coin theft. The thousands-of-nodes figure describes historical exposure, not the number still vulnerable.
Market impact
The disclosure concerns Bitcoin node security rather than a demonstrated loss of coins. Operators using packaged node software should check the Bitcoin Core version actually running and whether its whitelist range includes the Tor daemon's address.
Fixes shipped in Bitcoin Core 30.0, 29.2 and 28.3 in October 2025. The project recommends the latest maintenance release of the newest major version an operator can adopt. Its maintenance schedule covers 30.x, 31.x and 32.x; the 28.x and 29.x branches have reached end of life.

Frequently asked questions
-
Which Bitcoin nodes were affected by the Tor whitelist flaw?
Nodes were affected if they ran vulnerable Bitcoin Core software and used a non-default whitelist covering the IP address of their Tor daemon. Nodes without that setting were unaffected.
-
Why did Tor peers receive trusted connection permissions?
Bitcoin Core saw the Tor daemon's IP address rather than the remote peer's address. If the daemon's address matched the whitelist, incoming Tor connections inherited its trusted-peer permissions.
-
Did the Bitcoin Core flaw establish wallet access or coin theft?
No. The privileges described in the disclosure concerned network peer exemptions and do not establish wallet access or coin theft.
-
Which Bitcoin Core releases included the fix?
Bitcoin Core 30.0, 29.2 and 28.3 shipped with the fix in October 2025. The 28.x and 29.x branches have since reached end of life.
-
What should Bitcoin node operators check?
Operators should check the Bitcoin Core version actually running and whether their whitelist range includes the Tor daemon's address. The project recommends the latest maintenance release of the newest major version an operator can adopt.
 Lookonchain
 WuBlockchain
 TheBlock
 CoinTelegraph
 WatcherGuru
 CoinDesk