








 CryptoSlate


Polkadot's Community Foundation warned on Oct. 21 that the Fearless Wallet browser extension had been leaking users' private keys since February 2025, exposing DOT holders to unauthorized transfers for nearly 20 months. An investigation by the Polkadot Technical Fellowship found malicious code that harvested recovery phrases, private keys and keystore files whenever users unlocked their wallets, transmitting the data to an external server. Eight users have reported unauthorized transactions involving 17,286 DOT so far.
Why it matters
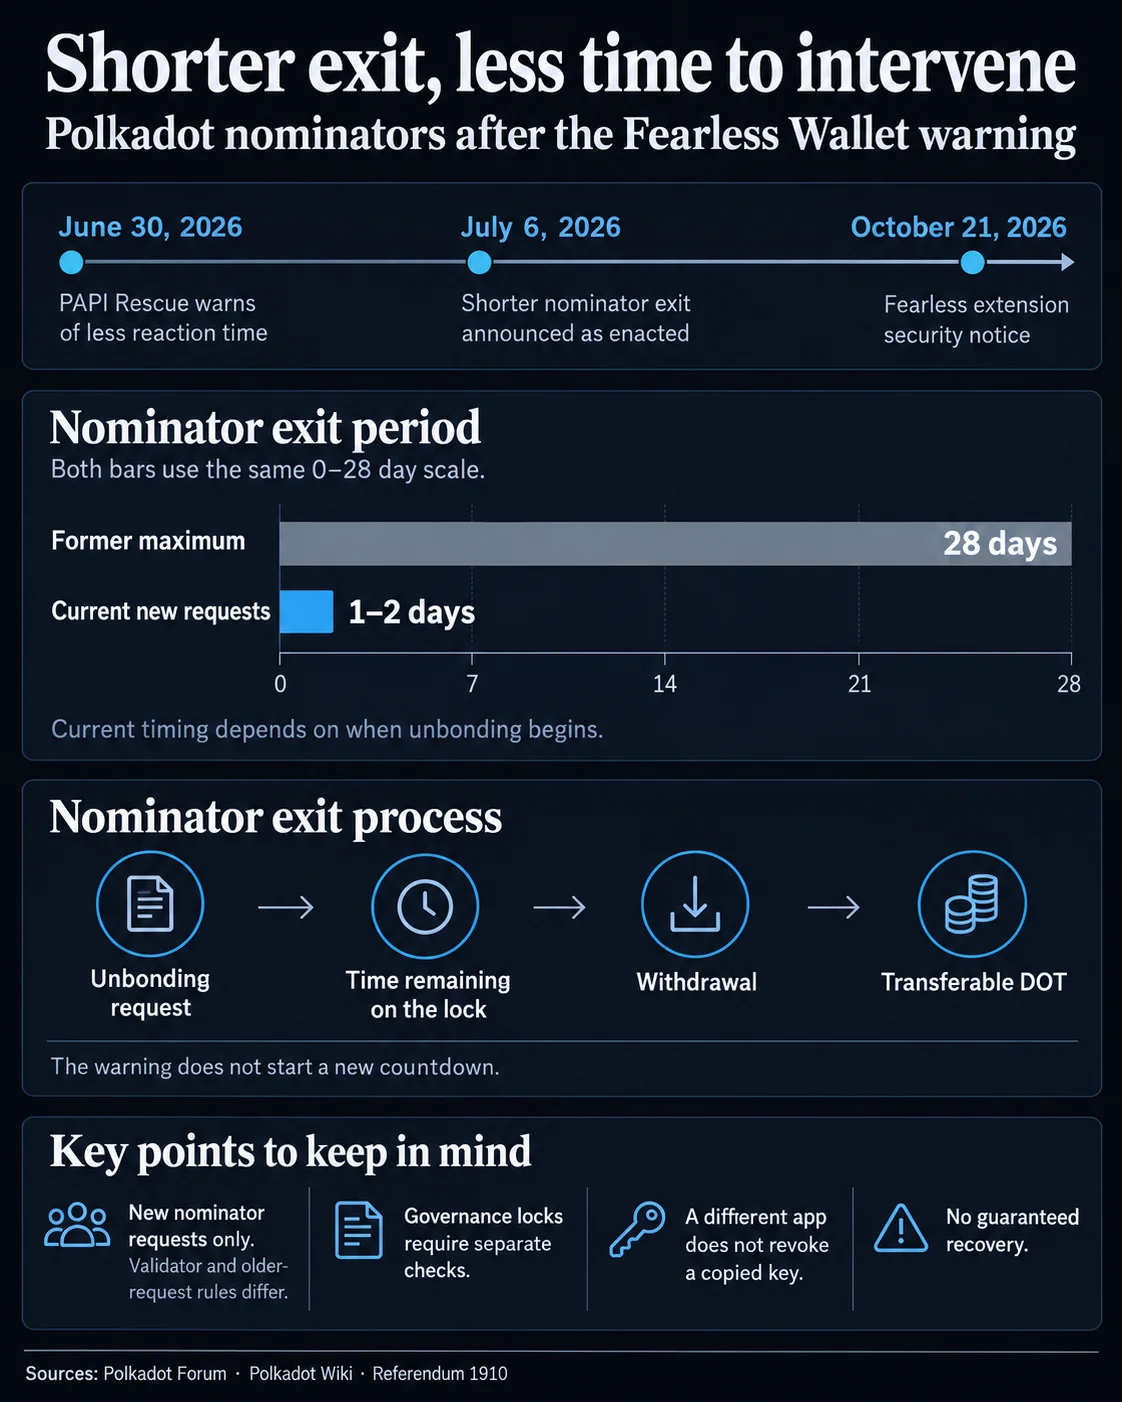
The disclosure landed three months after Referendum 1910 cut nominator unbonding from 28 days to as little as two, a liquidity win that also shrank the window to intervene in a compromised staking account before funds become transferable. Recovery service PAPI Rescue flagged exactly that risk on June 30, weeks before the change took effect on July 6 and months before Polkadot's alert. Blockchain security firm SlowMist traced the malicious behavior to extension versions 3.0.1 and 3.0.3 through 3.0.5, and found a remote configuration switch that let attackers toggle the theft on and off, making the compromise harder to spot. The offending code was removed from the source in June and the switch disabled in October, but neither change invalidates credentials already exposed.
Market impact
PAPI Rescue says it has recovered more than $250,000 in assets from compromised accounts, and the foundation is directing holders with locked or staked DOT to contact it before initiating any unstaking, since recovery options narrow sharply once funds are freely transferable. Affected users should generate an entirely new keypair with a different wallet rather than reusing the exposed recovery phrase, which leaves the underlying compromise unresolved. Watch for further loss reports as the breach window covers staking positions that may still be working through their unbonding schedules.
Frequently asked questions
-
Which Fearless Wallet versions were affected by the key leak?
SlowMist identified the malicious code in extension versions 3.0.1 and 3.0.3 through 3.0.5. The code collected recovery phrases, private keys and keystore files when users unlocked their wallets and sent them to an external server.
-
How much DOT was stolen in the Fearless Wallet breach?
Eight users have reported unauthorized transactions involving 17,286 DOT, according to the Polkadot Community Foundation's Oct. 21 disclosure.
-
Why does Polkadot's faster unstaking make the breach worse?
Referendum 1910 cut the nominator unbonding period from 28 days to roughly two, so compromised staked funds become transferable much sooner. That leaves recovery teams a far narrower window to intervene before an attacker can move the assets.
-
What should Fearless Wallet users do to protect their funds?
Create an entirely new keypair with a different wallet and move remaining funds immediately. Reusing the exposed recovery phrase, changing passwords or reinstalling the extension does not resolve the compromise.
-
What is PAPI Rescue and can it recover stolen Polkadot funds?
PAPI Rescue is a recovery service from the polkadot-api team that has recovered more than $250,000 from compromised accounts, with a 100% success rate among eligible cases. Holders with staked or locked DOT should contact it before unstaking, since options narrow once funds are transferable.
 CoinDesk
 WuBlockchain
 WatcherGuru
 CoinTelegraph
 CZ Binance
 TheBlock
 Lookonchain