








 CryptoSlate


Polymarket restored trading on Oct. 29 after a compromised third-party provider disrupted its international prediction market. Blockchain analytics firm Bubblemaps estimated that more than 700 users were affected and about $3.46 million in assets were compromised. Polymarket said it fixed the issue, referred it to law enforcement and would reimburse affected users, but its official notice did not specify total losses.
Why it matters
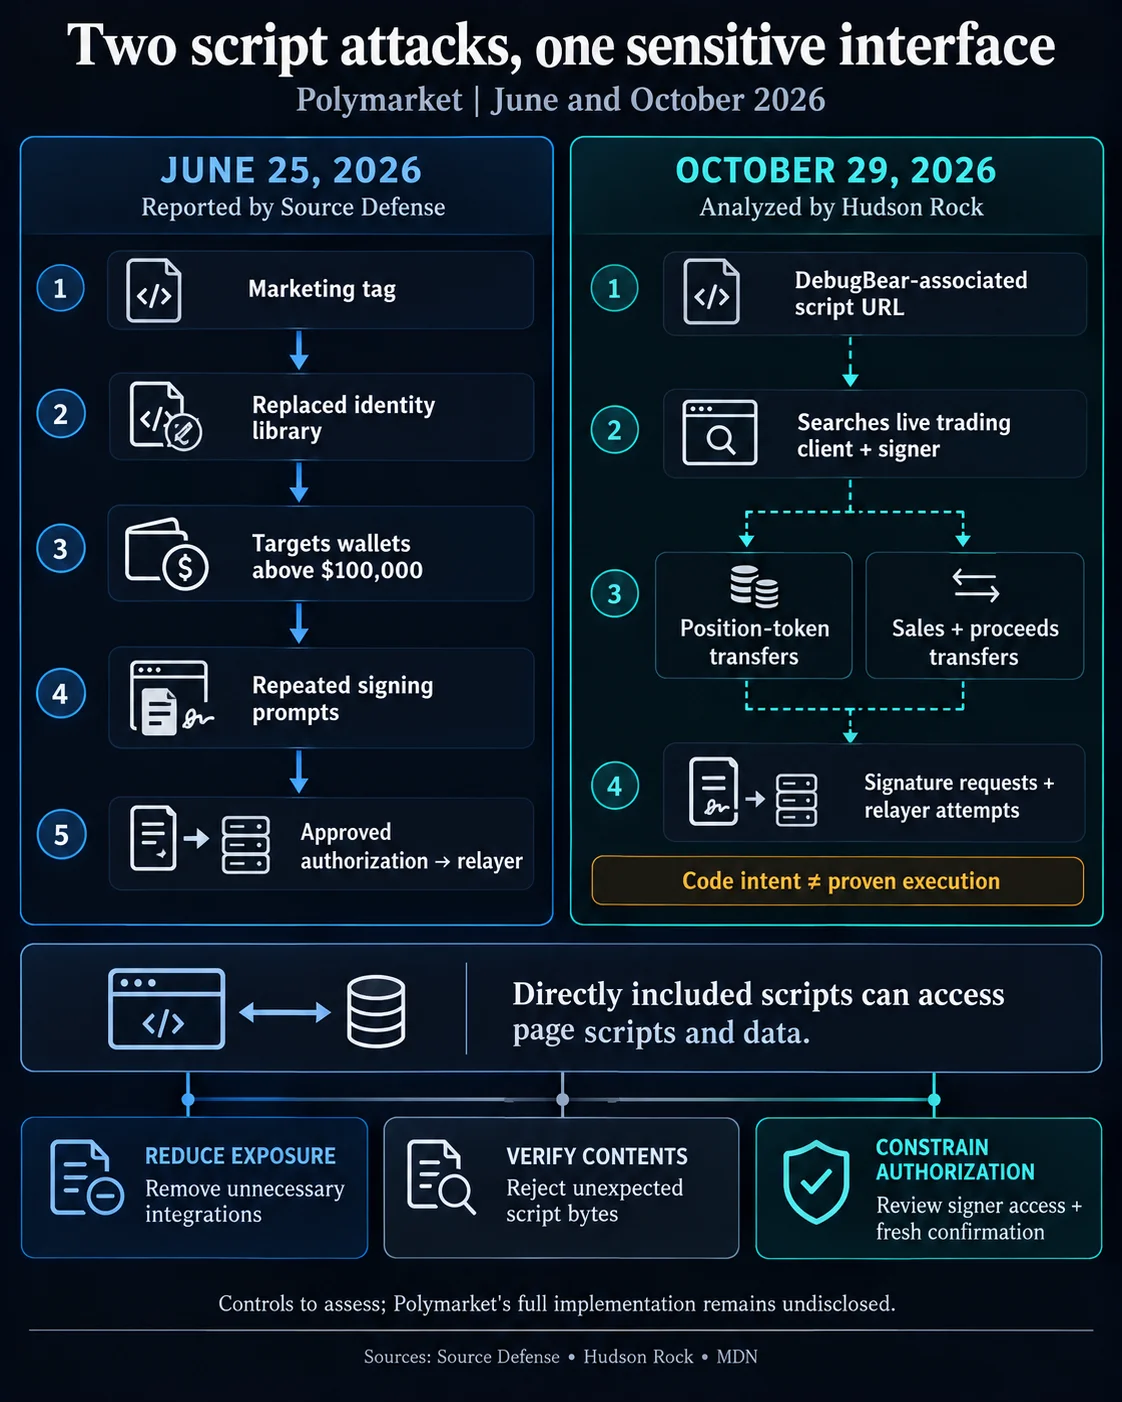
The October incident followed a June 25 website-script attack that reportedly drained about $3 million. Researchers describe different routes in the two incidents: June’s malicious script sought wallet authorizations, while code recovered from the October incident searched a logged-in session for trading tools and a signer that can request cryptographic authorization.
Hudson Rock’s static analysis found code programmed to request position-token transfers in one account branch, or sales and proceeds transfers in another. The researchers did not establish that the code executed, obtained silent signatures or stole private keys. The full victim-to-recipient trail also remained unproven, and removal metadata did not establish exactly when exposure ended.
Market impact
Bubblemaps estimated attackers converted roughly $2.7 million into POL and transferred it out, while about $750,000 remained on Polymarket at the time of its assessment. Those figures are an analytics firm’s estimate, not a total specified in Polymarket’s incident notice.
The repeat incidents put the security of trading interfaces in focus. Third-party scripts included directly in a webpage can access other page scripts and data; simply hosting a file elsewhere does not remove that access. Limiting outside code, constraining signer permissions and requiring fresh user confirmation for sensitive actions address different points in the risk chain. A detailed postmortem on exposure timing, affected accounts and authorization paths would help users assess what protections have changed.
Frequently asked questions
-
How much did Bubblemaps estimate was compromised in the October Polymarket breach?
Bubblemaps estimated that about $3.46 million in assets were compromised and more than 700 users were affected. Polymarket’s official notice did not specify total losses.
-
What did Polymarket say it would do for affected users?
Polymarket said it had fixed the issue, referred it to law enforcement and would make affected users whole.
-
How did the October code differ from the June attack?
The June attack reportedly used malicious code to seek wallet authorizations. October’s recovered code searched logged-in sessions for trading tools and a signer that can request cryptographic authorization.
-
What did researchers say remained unproven about the October code?
Hudson Rock’s static analysis did not establish that the code executed, obtained silent signatures or stole private keys. A complete victim-to-recipient trail also remained unproven.
-
What security measures could reduce the risks described in the incidents?
Limiting third-party code on trading pages, constraining signer permissions and requiring fresh user confirmation for sensitive actions address separate points in the risk chain.
 CoinDesk
 WuBlockchain
 CoinTelegraph
 Crypto Rank News
 TheBlock