


 CoinTelegraph
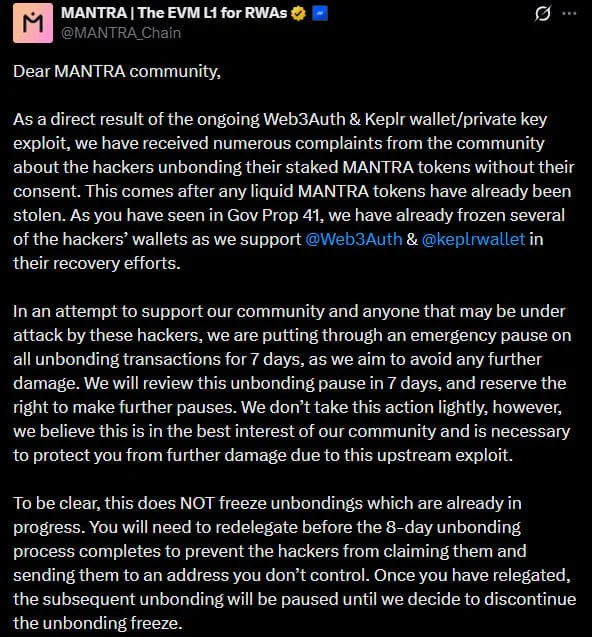
MANTRA says hackers have begun unstaking user tokens after a Web3Auth-Keplr wallet exploit put compromised keys to work, and the team has imposed an emergency seven-day pause on all unbonding to stop the drain.
Why it matters
The pause cuts both ways. It freezes the attacker's ability to walk stolen OM off the network, but it also locks every legitimate delegator out of their own withdrawal window for a full week. Anyone who needed liquidity on a schedule now has to wait out the freeze alongside the exploit response.
The attack vector is the softest spot in Web3 UX: the Web3Auth integration into Keplr wallets. Key management, not protocol logic, is where the funds leaked, which puts the burden on wallet infrastructure rather than on MANTRA's chain itself. Still, the fallout lands on the staking layer, and that is where the network had to intervene.
Market impact
Security incidents of this shape typically compress staking participation on the affected chain. Users who see unbonding suspended at the first sign of trouble tend to price that operational risk into future delegation decisions, and OM watchers should expect sentiment around the staking program to stay defensive until MANTRA details the scope of the compromise.
What to watch next: how many tokens the attackers managed to unstake before the pause took effect, whether MANTRA can claw back or block the exiting stake, and any statement on how many wallets were hit through the Web3Auth path.
Frequently asked questions
-
What caused the MANTRA staking incident?
A Web3Auth-Keplr wallet exploit compromised user keys, and hackers used that access to unstake tokens from affected wallets. The vulnerability was in wallet key management, not in MANTRA's chain logic.
-
Why did MANTRA pause unbonding for seven days?
MANTRA imposed an emergency seven-day unbonding pause to stop the attackers from completing unstakes and moving stolen OM off the network. The freeze blocks all delegators from withdrawing during that window.
-
Does the unbonding pause affect users who were not hacked?
Yes. The emergency freeze applies network-wide, so every delegator is locked out of withdrawals for the seven-day period, including wallets that were not compromised in the exploit.
-
Is the OM token itself vulnerable?
MANTRA identified the attack vector as the Web3Auth integration into Keplr wallets, which handles key management. The chain's staking protocol was not cited as the point of failure.
-
What should MANTRA stakers watch for next?
The key items are MANTRA's disclosure of how many wallets were affected, how many tokens the attackers unstaked before the pause took effect, and whether the network can block or claw back the exiting stake.
 TheBlock
 CryptoSlate
 WuBlockchain
 WatcherGuru
 CoinDesk