


 WuBlockchain
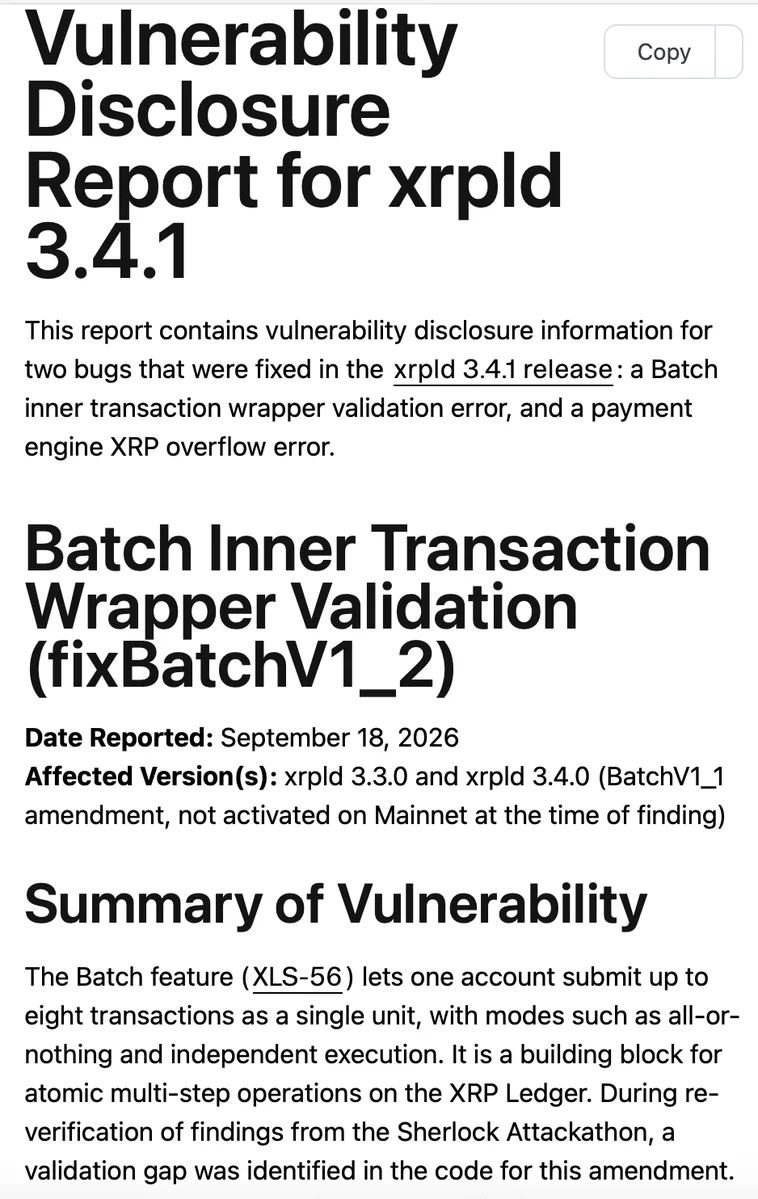
RippleX and the XRP Ledger Foundation disclosed a payment-engine overflow bug that could have allowed a specially crafted transaction to create spendable XRP beyond the network's fixed 100 billion supply. The flaw was present in code dating to 2015 and was fixed in xrpld 3.4.1 on September 25, when more than 80% of default validators upgraded.
Why it matters
Security researcher @Cayden_Liao said a proof of concept could mint about 18 trillion XRP in one transaction, roughly 184 times the intended supply. The vulnerability was reported through XRPL's bug bounty program, which paid the maximum $250,000 award.
Market impact
XRPL said it found no evidence that the flaw was exploited on a public network. The disclosure makes validator adoption and continued protocol-security work the key signals for XRP holders, while the fix preserves the ledger's stated supply rules.
Source: [Vulnerability Disclosure Report for xrpld 3.4.1](https://xrpl.org/es-es/blog/2026/vulnerabilitydisclosurereport-bug-20261009)
Frequently asked questions
-
What did the XRPL vulnerability allow an attacker to do?
A specially crafted transaction could have created spendable XRP beyond the XRP Ledger's fixed 100 billion supply.
-
How much XRP could the proof of concept have created?
Security researcher @Cayden_Liao said the proof of concept could mint about 18 trillion XRP in one transaction, roughly 184 times the intended supply.
-
When was the XRPL bug fixed?
The bug was fixed in xrpld 3.4.1 on September 25.
-
How widely did validators upgrade after the fix?
More than 80% of default XRPL validators upgraded on the day the fix was released.
-
Was the XRP Ledger bug exploited on a public network?
XRPL said it found no evidence that the vulnerability was exploited on a public network.
 CryptoSlate
 Crypto News
 WatcherGuru
 Glassnode
 CoinTelegraph
 CoinDesk
 TheBlock