


 CryptoSlate
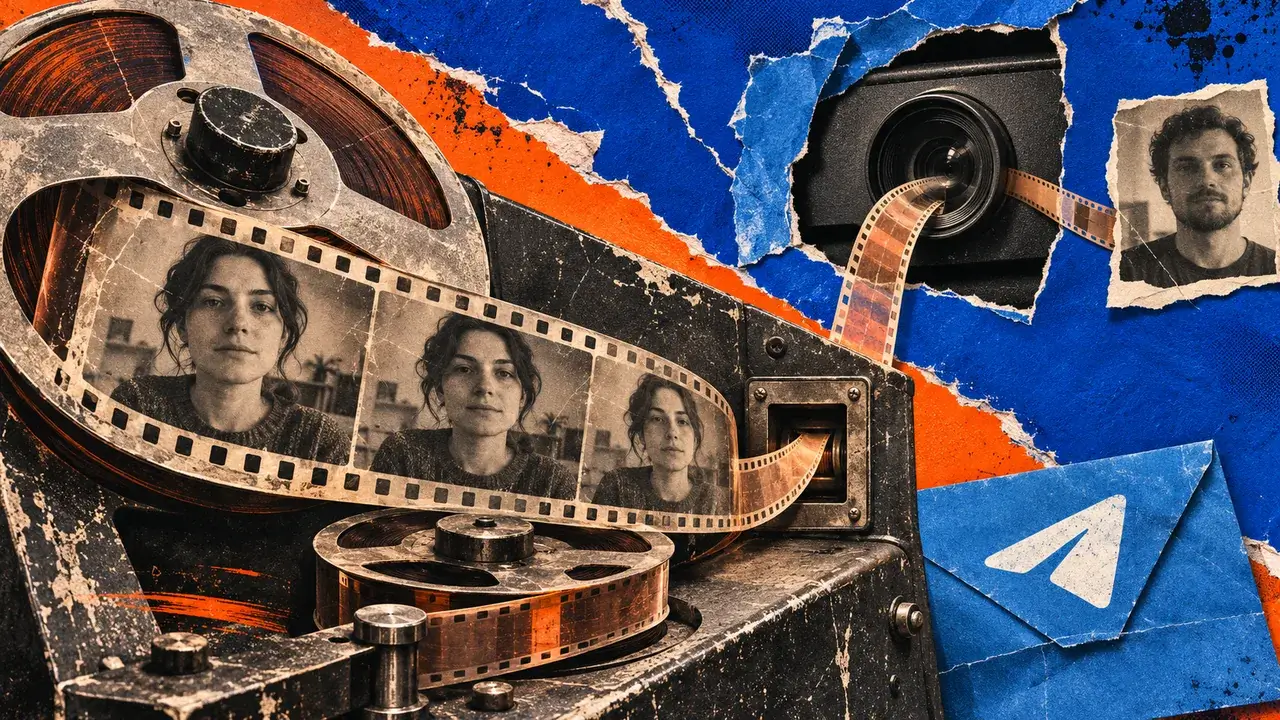
North Korean hackers have stolen more than $400 million in cryptocurrency over the past 18 months using a scheme the FBI calls FaceStealer, which hijacks real accounts and plays back stolen webcam footage to impersonate trusted contacts in fake meetings. The Justice Department announced on November 12 that it disrupted the cloud infrastructure behind the operation, and the FBI seized over 900 victim webcam videos under a federal warrant.
Why it matters
The attack chain is self-perpetuating. Attackers take over genuine accounts on Telegram, LinkedIn, Slack and Discord, use chat histories to craft convincing invitations, and route targets to copycat Zoom or Microsoft Teams sessions. Stored webcam footage makes it look like the known contact joined the call, and recording of the new target begins the moment they click the imposter link. That footage becomes material for the next approach.
The malware installed through a fake technical fix can harvest browser cookies, log keystrokes, capture screens and maintain access to the device. The FBI reported cases where cryptocurrency theft and account takeovers surfaced months to more than a year after the initial compromise, so a quiet period after a suspicious meeting does not mean a device is safe.
Market impact
The FBI advises confirming invitations through a separate communication channel, using the official meeting app with an invite code, delaying webcam activation, and refusing any script or terminal code presented as a video-client update. Suspected victims are told to move funds to a new wallet created on an unaffected device, secure developer and communication accounts, alert contacts and employers, and report to IC3 with the keyword FaceStealer. The operation was handled separately from the Binance theft the FBI has previously attributed to North Korean actors.
Frequently asked questions
-
What is the FaceStealer crypto scam the FBI warned about?
FaceStealer is a North Korean-linked scheme that hijacks real communication accounts, lures contacts into fake Zoom or Teams meetings using stolen webcam footage, and installs malware through a fake technical fix. The FBI says it caused over $400 million in cryptocurrency theft over 18 months.
-
How did the FBI and Justice Department disrupt FaceStealer?
On November 12 the Justice Department announced disruption of the cloud-based infrastructure used in the scheme, and the FBI seized over 900 victim webcam videos under a federal warrant.
-
Why does a fake video call look so convincing in this scam?
Attackers play back webcam recordings of a real prior victim, so the familiar face on screen is not a live participant. The scheme overwhelmingly relies on stolen genuine videos, with generated deepfakes as an additional impersonation method.
-
How does the malware get installed during the fake meeting?
An attacker claims an audio or technical problem and offers an update prompt, a script, or code to paste into a terminal. Following those instructions installs malware that can harvest cookies, log keystrokes, capture screens and maintain access to the device.
-
What should you do if you suspect you were compromised by FaceStealer?
Move cryptocurrency to a new wallet created on an unaffected device, secure communication and developer accounts, alert contacts and employers, and report to IC3 with the keyword FaceStealer. Theft can surface months to over a year after the initial compromise.
 Crypto News
 CoinTelegraph
 WuBlockchain
 TheBlock