


 WuBlockchain
Bitget CEO Gracy Chen has formally asked THORChain to reject transactions from addresses linked to Bitget’s recent security incident. The addresses have been publicly flagged and remain under active surveillance, she said.
Why it matters
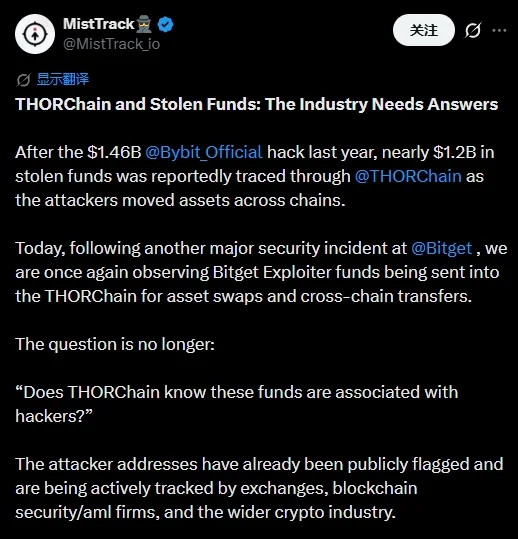
The request follows MistTrack’s warning that funds from the Bitget incident are moving through THORChain for asset swaps and cross-chain transfers. MistTrack also pointed to an earlier Bybit exploit, in which nearly $1.2 billion in stolen funds was routed through the protocol.
Chen argued that decentralization is a design principle, not a shield for facilitating the movement of known stolen funds. MistTrack likewise called for the industry to discuss what responsibility THORChain should bear when handling assets from publicly identified exploits.
Market impact
The dispute raises a governance and security question for cross-chain infrastructure: whether a protocol should reject transactions associated with publicly flagged addresses. The source identifies no response from THORChain, leaving its position on Chen’s request unclear.
Frequently asked questions
-
What did Gracy Chen ask THORChain to do?
Chen formally asked THORChain to reject transactions originating from addresses linked to Bitget’s recent security incident.
-
Why are the attacker addresses identifiable?
Chen said the addresses have been made public and remain under active surveillance.
-
How are funds from the Bitget incident reportedly moving?
MistTrack says funds are flowing through THORChain for asset swaps and cross-chain transfers.
-
What earlier exploit did MistTrack cite?
MistTrack cited the Bybit exploit, in which nearly $1.2 billion in stolen funds was routed through THORChain.
-
What responsibility question does the dispute raise?
It raises whether decentralized protocols should reject transactions from publicly flagged addresses linked to known exploits.
 CoinDesk
 Lookonchain
 TheBlock
 CoinTelegraph