


 WuBlockchain
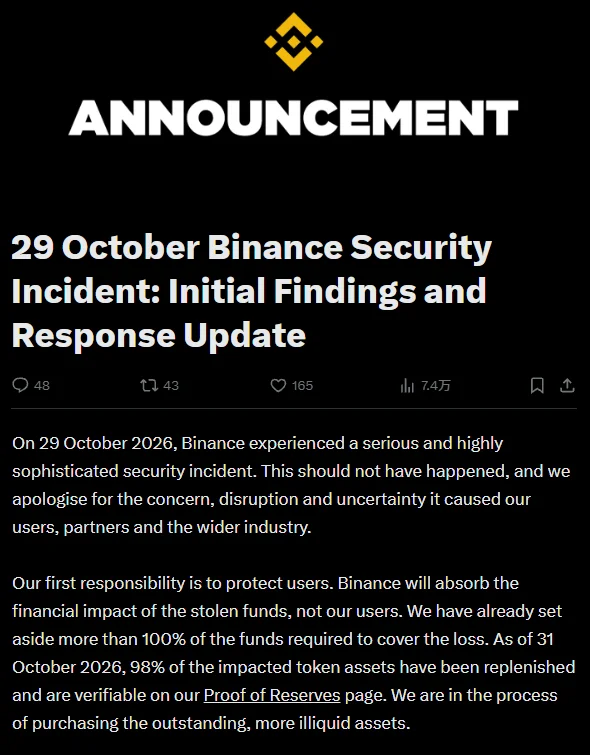
Binance's initial report says attackers used fake job interviews to plant malware on an engineer's device in September, then exploited an internal AI tool to reach wallet engineers. Stolen credentials gave them access to a wallet signing service, and they abused Ethereum's EIP-7702 authorization mechanism in a hack involving $6.34 billion in assets.
Why it matters
Binance said suspending withdrawals alone could not stop the malicious on-chain authorizations. Stopping them required a separate revocation process, highlighting a security gap beyond ordinary withdrawal controls.
Market impact
About $2.85 billion of affected assets has been frozen or intercepted. Binance said 98% of affected token assets had been replenished by October 31 and that it had set aside sufficient funds to cover all losses. The investigation remains ongoing.

Frequently asked questions
-
How did attackers first gain access to Binance's wallet engineers?
Binance says attackers used fake job interviews to plant malware on an engineer's device, then exploited an internal AI tool to reach wallet engineers.
-
Why did suspending withdrawals not stop the malicious authorizations?
Binance said the on-chain authorizations required a separate revocation process, so suspending withdrawals alone could not stop them.
-
What role did Ethereum's EIP-7702 play in the hack?
Attackers abused Ethereum's EIP-7702 authorization mechanism after compromising a wallet signing service with stolen credentials.
-
How much of the affected assets has been frozen or intercepted?
Binance said approximately $2.85 billion of the $6.34 billion in affected assets had been frozen or intercepted.
-
What did Binance say about covering losses?
Binance said 98% of affected token assets had been replenished by October 31 and that sufficient funds were set aside to cover all losses.
 TheBlock
 CryptoSlate
 WatcherGuru
 CoinDesk
 CoinTelegraph
 Lookonchain