


 WuBlockchain
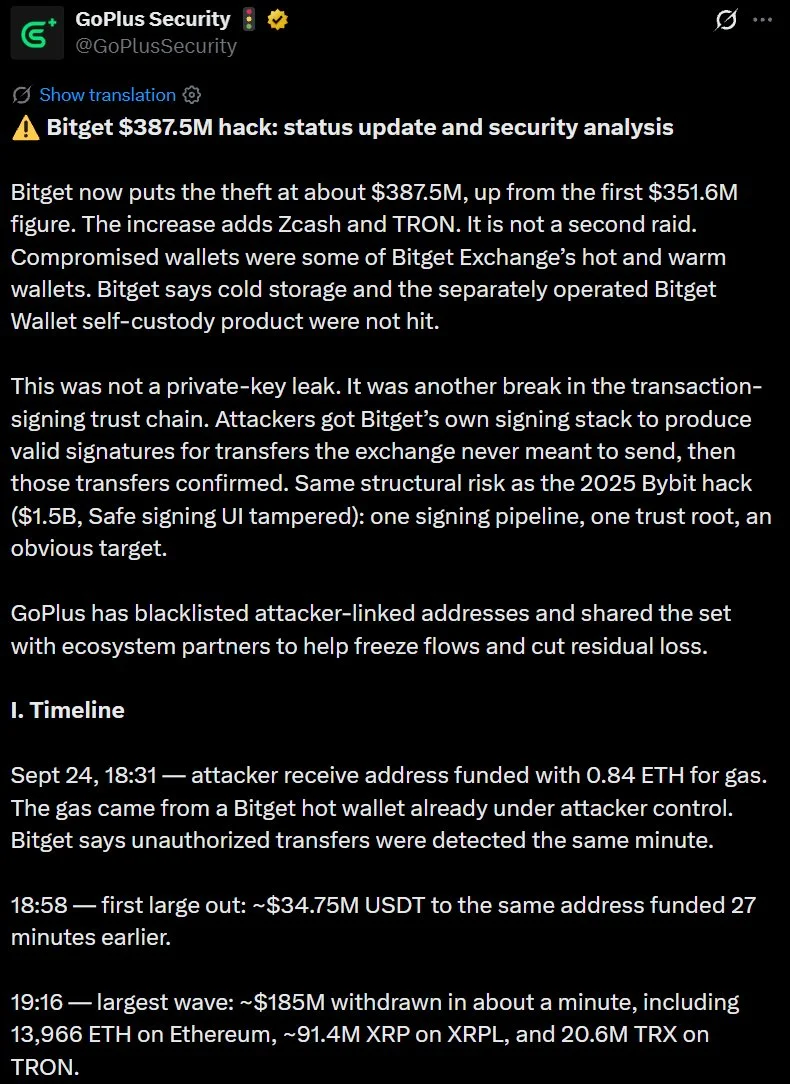
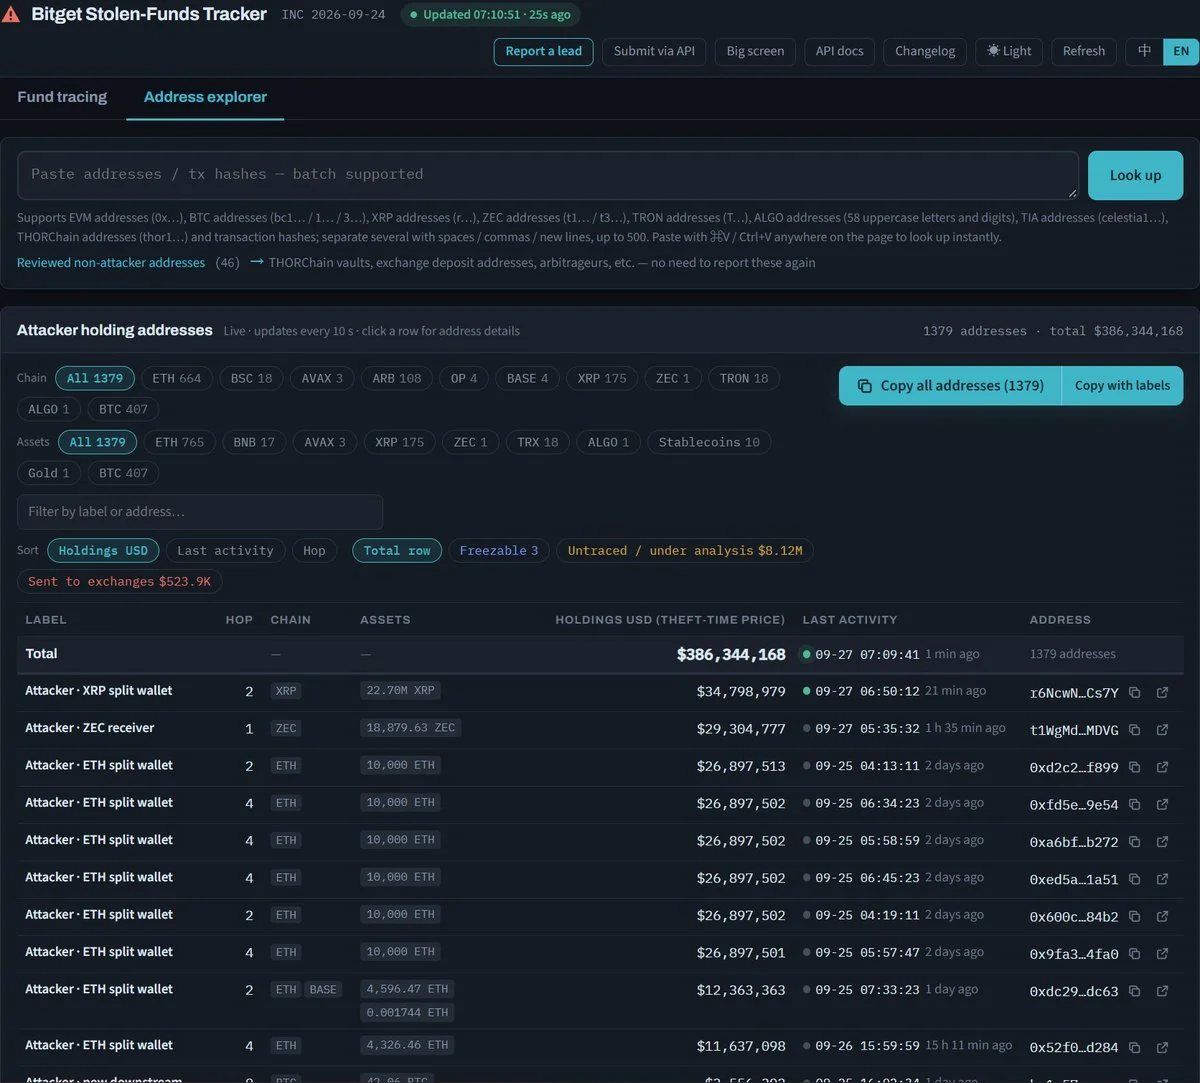
GoPlus Security's review of the $387.5 million Bitget hack found the attack did not involve a private-key leak. Instead, attackers breached a critical wallet backend system, forged transaction data, and tricked Bitget's authorized signing flow into generating valid signatures for transfers the exchange never intended to make.
The fund-drain window lasted roughly 2 hours and 25 minutes, with the largest single wave moving about $185 million in around one minute. GoPlus has blacklisted attacker-linked addresses and shared them with ecosystem partners.
Why it matters
The finding shifts the threat model: even exchanges that never expose private keys can be drained if the transaction-signing trust chain is compromised. GoPlus noted structural similarities to the 2025 Bybit hack, suggesting supply-chain attacks on wallet infrastructure are becoming a repeatable playbook.
Bitget has not yet published a full technical report, and the initial intrusion method remains unconfirmed.
Market impact
Attention now turns to whether other venues audit their signing backends and how Bitget covers the shortfall. The fastest-moving $185 million wave in a single minute shows how little reaction time security teams get once signing infrastructure is compromised.
Frequently asked questions
-
How did hackers drain $387.5M from Bitget without leaking private keys?
GoPlus found attackers breached a wallet backend system and forged transaction data, causing Bitget's authorized signing flow to generate valid signatures for transfers the exchange did not intend to make.
-
How long did the Bitget hack fund-drain last?
The drain window lasted approximately 2 hours and 25 minutes, with the largest wave moving roughly $185 million in about one minute.
-
Is the Bitget hack similar to the Bybit hack?
GoPlus said the incident shows structural similarities to the 2025 Bybit hack, though Bitget has not yet published a full technical report and the initial intrusion method remains unconfirmed.
-
What is a transaction-signing trust chain attack?
It is an attack that compromises the systems that prepare and authorize transactions rather than the private keys themselves, tricking the legitimate signing flow into approving malicious transfers as if they were valid.
-
What has been done about the attacker addresses?
GoPlus has blacklisted attacker-linked addresses and shared them with ecosystem partners to help freeze or trace the stolen funds.
 CoinDesk
 Lookonchain
 Crypto Rank News
 CryptoSlate
 WatcherGuru